audit
Exposes the framework’s event store as a paginated, filterable audit log via the audit:query:list handler (accessible to Admin and SystemAdmin roles). Write history comes from the event store: every entity write already records who, when, what entity, and the event payload with PII stripped. A SystemAdmin can pass scope: "system" to read the app-instance system events such as app.started, and reads the events of every tenant (system tenant excluded) through audit:query:list-all-tenants and the audit-log-all-tenants screen. Filter by aggregateType, aggregateId, eventType, userId, or time range. Also records audit:event:escape-hatch-used whenever a handler uses one of the framework’s escape hatches (unsafeRaw, acknowledgeCrossTenant, db.global() writes, or a granted identity switch). Read accesses that need proof (e.g. a portal link opened) are recorded with recordAccess(ctx, { subjectType, subjectId, action, details }) from @cosmicdrift/kumiko-bundled-features/audit into the store_access_log table outside the caller’s transaction, readable by admins through audit:query:access-log and pruned per tenant after the compliance profile’s audit-log retention (minimal profile without compliance-profiles) by the maintenance job audit:job:access-log-retention.
Live preview
Section titled “Live preview”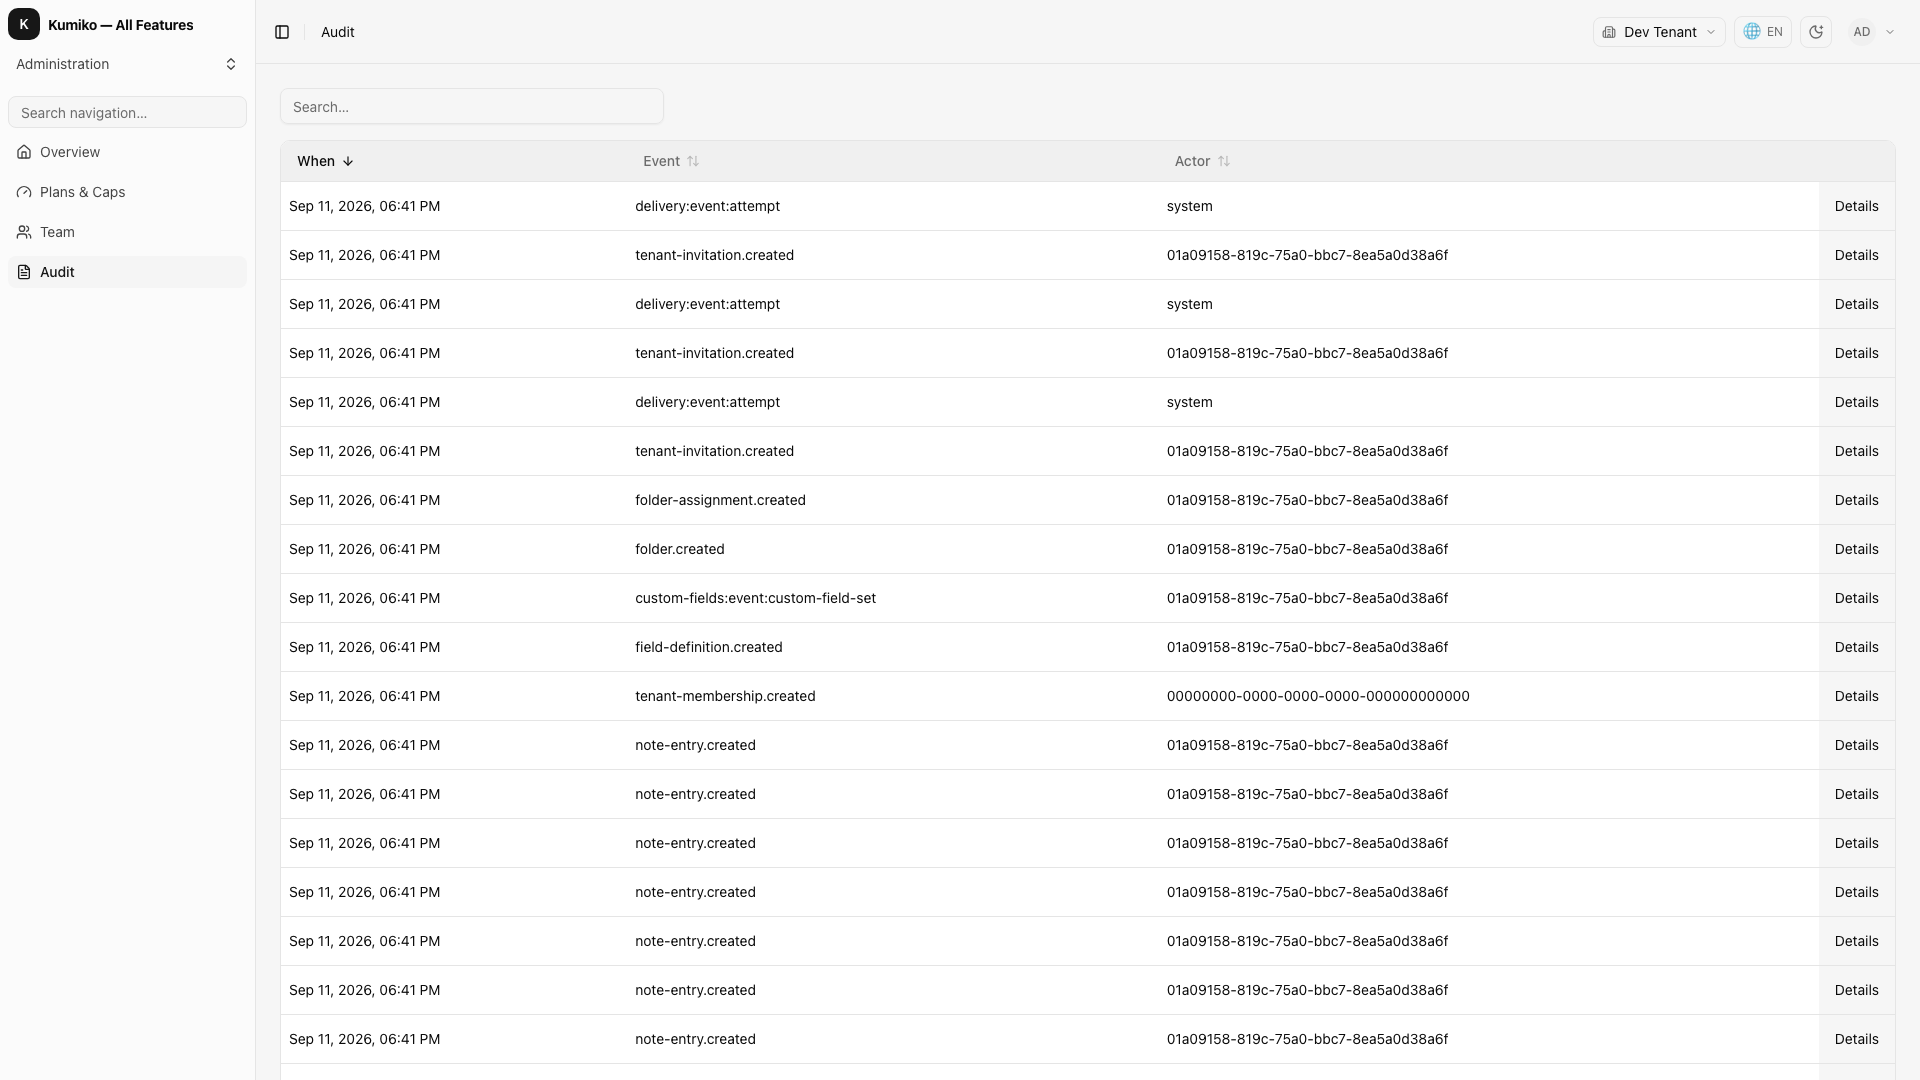
How it fits
Section titled “How it fits”What this feature needs to run (Requires).
flowchart TB
  n_audit["audit"]
  subgraph how_reqs["Requires"]
    n_tenant["tenant"]
    n_user["user"]
    n_config["config"]
  end
  n_tenant --> n_audit
  n_user --> n_audit
  n_config --> n_audit
Getting started
Section titled “Getting started”Start with apps-admin-console for a step-by-step walkthrough with runnable code and integration tests.
Dependencies
Section titled “Dependencies”Configuration
Section titled “Configuration”Per-tenant config keys, set via the tenant-admin UI or a seed. 🔒 = encrypted at rest.
| Key | Type | Default | Scope | Who can write | Who can read |
|---|---|---|---|---|---|
escape-hatch-retention-days | number (≥ 1) | 90 | system | system | TenantAdmin, Admin, SystemAdmin |